
Astra Security Releases Free Tools to Help Organizations Find and Fix PHP2Shell Vulnerabilities
Astra Security Releases Free Tools to Help Organizations Find and Fix PHP2Shell Vulnerabilities
PR Newswire
CLAYMONT, Del., Oct. 23, 2026
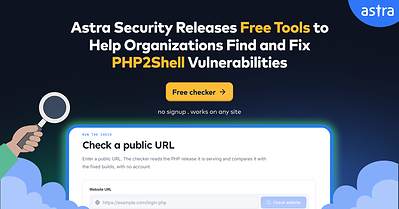
CLAYMONT, Del., Oct. 23, 2026 /PRNewswire/ -- Astra Security today released two free resources for organizations responding to PHP2Shell, the critical PHP vulnerabilities disclosed this week. The first is a public-URL PHP2Shell Checker. The second is php2shell-triage, an open-source skill for deeper investigation.
The flaws, CVE-2026-109618 and CVE-2026-109619, are each rated 9.2 on CVSS v4.0 and can allow unauthenticated remote code execution through PHP's core runtime. Fixes are available in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP runs across websites, CMS platforms, custom applications and vendor-managed infrastructure, so many organizations will need to look beyond the applications they maintain directly.
Start with what's public: Scan Public Assets with the PHP2Shell Checker
The PHP2Shell Checker compares the PHP version a public website appears to serve against the fixed releases. It needs no account. The result is a first signal, not a verdict: proxies, hosting providers and server settings can hide or alter version information, and a clean result says nothing about internal systems.
Go deeper on systems you run: Assess Internal Systems with php2shell-triage
php2shell-triage helps teams assess PHP runtimes across server APIs, flag stale workers, look for indicators of exploitation, and plan remediation for PHP vulnerabilities. Its read-only script inspects the binaries behind running PHP workers instead of trusting the command-line version. That catches servers that report a patched PHP while old workers are still serving the vulnerable runtime, preventing unauthenticated remote code execution (RCE).
How to Fix PHP2Shell: Immediate Remediation Steps
Identify affected installations, apply updates, restart PHP workers, and verify that the patched runtime is running. Where compromise is suspected, capture evidence before restarting. End-of-life versions (8.1 and earlier) will not receive official fixes and need an upgrade plan. Where patching isn't immediately possible, consider isolating vulnerable systems.
"During a disclosure like PHP2Shell, the hardest question isn't 'Are we vulnerable?' It's 'What is actually running right now?'" said Shikhil Sharma, Founder & CEO at Astra Security.
Free tools
PHP2Shell guidance
Related advisories from this week
- LiteLLM supply-chain attack
- GitLab CVE-2026-110264, a critical CVSS 10.0 regex RCE
- Node.js October 2026 security patches
- Railway breach: what to rotate and what rotation won't fix
Watch

SOURCE Astra Security

The articles, information, and content displayed on this webpage may include materials prepared and provided by third parties. Such third-party content is offered for informational purposes only and is not endorsed, reviewed, or verified by Morningstar.
Morningstar makes no representations or warranties regarding the accuracy, completeness, timeliness, or reliability of any third-party content displayed on this site. The views and opinions expressed in third-party content are those of the respective authors and do not necessarily reflect the views of Morningstar, its affiliates, or employees.
Morningstar is not responsible for any errors, omissions, or delays in this content, nor for any actions taken in reliance thereon. Users are advised to exercise their own judgment and seek independent financial advice before making any decisions based on such content. The third-party providers of this content are not affiliated with Morningstar, and their inclusion on this site does not imply any form of partnership, agency, or endorsement.
Popular

These Overvalued Stocks Have Plenty of Room to Fall
3 of the Best Dividend Stocks to Own
3 Stocks to Sell and 3 Stocks to Buy for November
4 Big Impacts from the US Midterm Elections for Investors

 United States